Continuous Monitoring for the Speed of Modern Software Development
Security leaders have a timing problem. Software changes faster than the processes built to verify it. Systems get patched, rebuilt, and pushed live by the hour, while authorization decisions still rely on evidence gathered months ago.
You can't secure a system moving at machine speed with a process stuck in calendar time.
What keeps CISOs awake
- AI-driven attacks move in minutes. Threat actors use automated tooling that can compromise a network in under five minutes. If your security posture is based on a quarterly review, you're defending against a ghost.
- Configuration drift is invisible. A system that passed its January audit isn't the same system in March. A base image gets swapped or a permission gets widened to unblock a release and never tightened back down. It rarely trips an alarm, but it creates exposure.
- Tool sprawl kills visibility. Every pipeline relies on a patchwork of third-party containers, open-source libraries, and multiple scanners — each speaking its own language. Reconciling them by hand bogs down engineering teams.
- AI demands speed. Mission owners want AI capabilities deployed now. But because authorization still depends on manual evidence collection, security leaders are forced into an impossible choice: slow down delivery or accept undocumented risk.
Traditional audits used to argue for Authorization to Operate (ATO) are point-in-time snapshots. They can't keep pace with systems that change continuously.
From snapshot audits to continuous monitoring
Continuous monitoring doesn't happen by bolting on a single tool. It requires a unified pipeline that automates evidence collection from code to cloud.
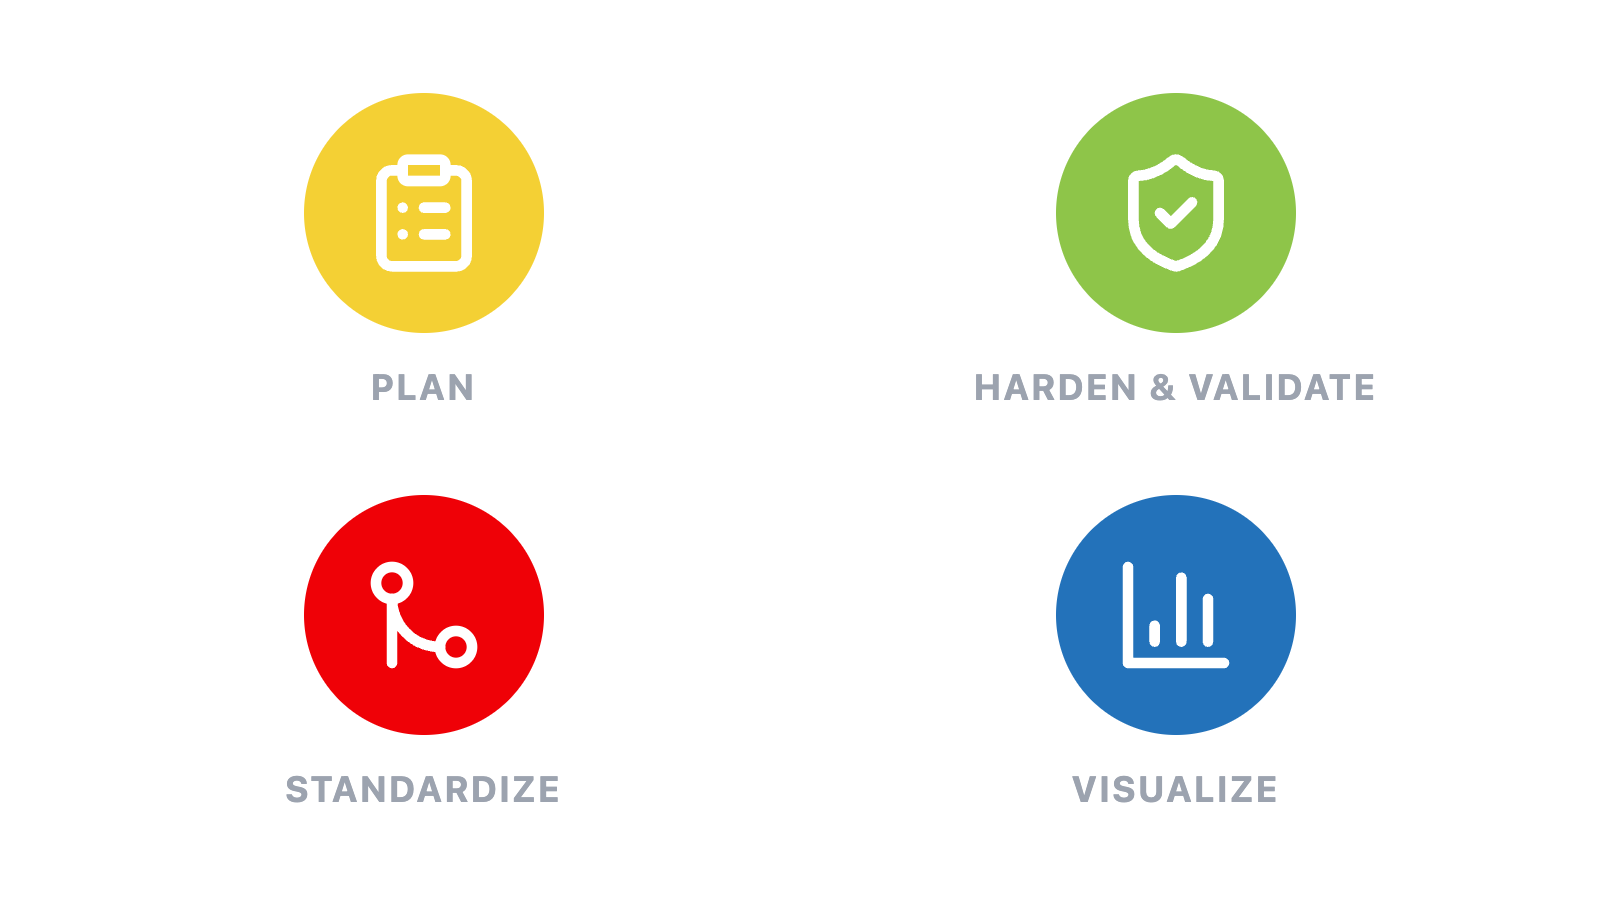
That's why we built the Aesir Systems Automation Platform™. Four connected products carry compliance from design to audit:
- Plan with Sindre™: We turn government and industry benchmarks into actionable configuration guidance. Define what "secure" means before deployment so you stop vulnerabilities before they hit code.
- Harden and Validate with Automation Content™: Continuous InSpec and Ansible profiles lock down containers, platforms, and OS layers wherever they live, flagging drift the moment it happens.
- Translate with Bifrost™: Bifrost normalizes output from your existing scanners into the Heimdall Data Format. You don't have to rip and replace your security stack; Bifrost makes your current investments actually work together.
- Visualize with Vara™: Vara ingests more than 50 scanner formats and streamlines them into a single, real-time dashboard. Track posture, prioritize remediation, and ditch periodic spreadsheet drills.
Evidence that builds itself
Because these tools talk to each other, compliance documentation builds itself in the background. Evidence is captured as events happen, aligning directly with NIST SP 800-53A Rev 5.
For your program, that means practical outcomes:
- Lower audit risk because your evidence reflects the system running today, not months ago.
- Shorter re-authorization cycles.
- Drift caught and fixed before it turns into a breach.
- A clear, automated path from initial ATO to continuous ATO (cATO).
Aesir cuts the path to ATO by up to 80%, slashing costs and months of delay.
Next steps
If your program is trying to authorize faster without taking on blind risk, it's time to move to continuous monitoring. Reach out to our team at contact@aesirsystems.com to see where your evidence pipeline stands.